
Scope
Align on objectives, systems, and testing scope.
We define goals, in-scope assets, constraints, timelines, and success criteria so testing stays focused and measurable.
Process
Our process is collaborative and practical—designed to produce actionable outcomes without unnecessary noise.
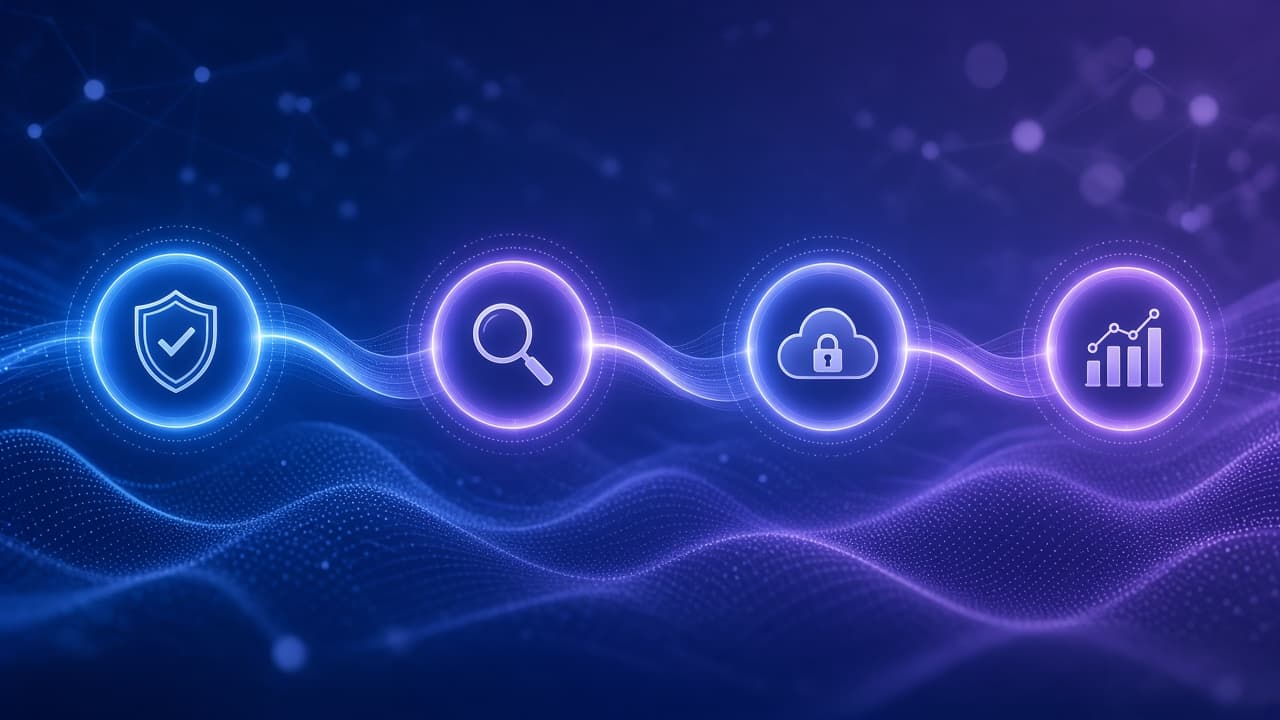
Four stages. One goal: help you reduce risk with confidence.
Align on objectives, systems, and testing scope.
We define goals, in-scope assets, constraints, timelines, and success criteria so testing stays focused and measurable.
Identify and validate security weaknesses.
Our team combines targeted automation with manual testing to uncover and validate issues that matter in real attack scenarios.
Review prioritized findings and their impact.
You receive a formal VAPT Report with business impact, evidence, severity, and remediation guidance your teams can act on immediately.
Verify that the fixes resolve the findings.
After remediation, we retest agreed findings and issue a Letter of Attestation (or closure report) confirming what was verified.
Formal outputs
Penetration testing does not issue an official security certification for your app. Instead, Digital Software Labs provides a formal VAPT Report and a Letter of Attestation (or closure report) after testing and retesting your application.
A formal VAPT Report documenting validated findings, risk ratings, evidence, and remediation guidance for your application or environment.
A formal letter confirming retesting outcomes and closure status for remediated findings—not an official security certification of your app.
A VAPT Report and Letter of Attestation document testing outcomes and retest closure. They are not an official security certification that your application is free from all vulnerabilities.
You stay informed. We stay focused. Findings stay useful.
Shared objectives, rules of engagement, and success criteria before testing begins.
Critical issues can be escalated early so your team can act while testing continues.
A structured walkthrough of findings, priorities, remediation, and retest closure.
Share your environment and we’ll recommend the right assessment shape.